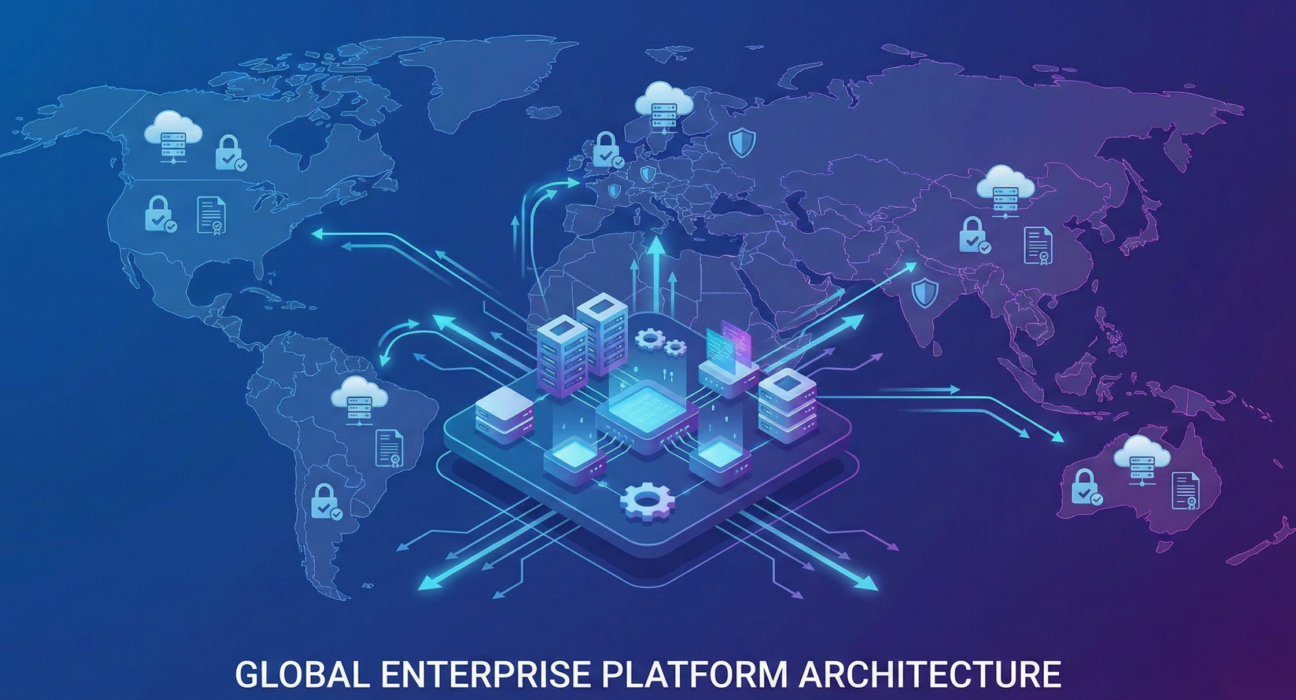
When a large enterprise decides to expand its digital platform across multiple countries, the initial planning often focuses on technical architecture, user experience, and speed to market. These are important. But experienced technology leaders know that one issue will surface repeatedly and create more complexity than anticipated: local compliance requirements.
Every country has its own rules about data residency, privacy, consumer protection, taxation, and industry-specific regulations. These rules are not suggestions. They carry legal and financial consequences. What works in one market may be restricted or illegal in another. The challenge is not just understanding these rules. The real challenge is building a platform that can operate efficiently across all markets while respecting every local constraint without creating a fragmented, unmaintainable system.
Why This Problem Gets Harder at Scale
A platform serving two or three countries can often handle compliance through configuration or manual processes. Teams can manage exceptions, keep track of variations, and adjust workflows as needed. But when the platform expands to ten, fifteen, or thirty countries, this approach breaks down.
The complexity grows in multiple dimensions. Different countries require different data storage locations. Some prohibit certain types of data from leaving their borders. Others have specific rules about user consent, cookie tracking, or marketing communications. Payment processing regulations vary widely. Tax calculations become complicated. Customer service requirements differ. Industry certifications may be mandatory in some regions but not in others.
Each new market adds another layer of requirements. Engineering teams start building custom code for each country. Configuration files become difficult to manage. Testing becomes more time-consuming. Deployment processes slow down. The platform that was supposed to create efficiency across markets becomes a collection of country-specific workarounds.
The operational risk increases as well. A compliance failure in one country can trigger regulatory action, financial penalties, or reputational damage. When a platform operates across many jurisdictions, the probability of an oversight increases. Legal teams in different regions may interpret requirements differently. What one team considers compliant, another may view as risky.
Governance becomes harder too. Who approves changes that affect multiple countries? How do you ensure that a feature update in the core platform does not violate a local rule? How do you track which version of the platform is running in which country and whether it meets current regulations?
These are not abstract problems. They are the daily reality for technology leaders managing multi-country platforms.
The Architectural Decision That Defines Everything
The most important decision is whether to build a single shared platform with localization capabilities or separate platforms for different regions. Both approaches have trade-offs.
A single platform with built-in flexibility offers cost efficiency and faster feature deployment. You maintain one codebase, one infrastructure, one team. Changes roll out to all markets at once. But this approach requires significant upfront investment in architecture. The platform must be designed to handle variations in compliance, language, currency, payment methods, and user behavior. If the design is not flexible enough, you end up forcing exceptions into a system that was not built for them.
Separate platforms for different regions give you maximum control and compliance certainty. Each platform can be tailored exactly to local requirements. But the cost is high. You duplicate effort. Teams in different regions build similar features independently. Maintenance becomes expensive. Knowledge does not transfer easily. Feature parity becomes difficult to maintain.
Most large enterprises end up somewhere in the middle. They build a core platform with strong localization capabilities and allow controlled regional customization. This works, but only if the architecture is planned correctly from the start and governance is clear.
The architecture must separate concerns properly. Core business logic should be independent of compliance logic. Data storage, processing, and movement should be controlled by policies that can be configured per country. User interfaces should adapt to local languages, formats, and legal requirements without requiring code changes.
This requires discipline. It also requires teams who have done this before and know where the problems will appear.
Data Residency and Cross-Border Transfers
Data residency rules are among the most complex compliance constraints. Some countries require that certain types of data must be stored within their borders. Others allow data to be transferred out but only under specific conditions. Some require user consent for cross-border transfers. Others have different rules for different types of data.
A platform serving multiple countries needs a clear data strategy. Where will customer data be stored? Where will transaction records be kept? Where will analytics and reporting data live? How will the platform handle users who access services from multiple countries?
The technical implementation is not trivial. You need infrastructure in multiple regions. You need routing logic that directs data to the correct location based on user location, data type, and applicable regulations. You need synchronization mechanisms when data needs to be accessed across regions. You need audit trails that prove compliance.
You also need to think about performance. If data must stay in a specific country, your application architecture must minimize cross-region calls. Users expect fast response times. Latency increases when every operation requires a round trip to a distant data center.
And you need to plan for change. Data residency rules are not static. Governments update regulations. New rules are introduced. What is allowed today may be restricted tomorrow. The platform must be built to adapt without requiring a complete redesign.
How Ozrit Approaches Multi-Country Platform Delivery
Ozrit works with enterprises that need to build or scale platforms across multiple countries with complex compliance requirements. The approach is different from typical consulting or offshore development models.
The first difference is senior involvement. Ozrit assigns an engagement lead who stays with the program from start to finish. This is not a sales handoff. The lead is an experienced technology professional who understands enterprise delivery, compliance constraints, and how to navigate organizational complexity. They own the relationship and the outcome.
The second difference is how Ozrit structures the team. Multi-country platforms require people who understand both the technical architecture and the regulatory environment. Ozrit assembles teams that include engineers who have built similar systems before, compliance specialists who know how to interpret and implement regulations, and delivery managers who can coordinate work across time zones and stakeholder groups.
The third difference is onboarding discipline. Ozrit does not start building immediately. There is a structured onboarding phase where the team learns the enterprise’s systems, compliance requirements, existing architecture, and organizational constraints. This reduces risk. It ensures that the team understands the context before making decisions that are expensive to reverse.
Timelines are realistic. A multi-country platform is not a three-month project. Depending on scope and complexity, delivery typically takes six to eighteen months. Ozrit plans in phases. Early phases focus on core architecture, data strategy, and compliance foundations. Later phases add countries, features, and integrations. This approach allows the enterprise to validate the architecture before committing to full-scale rollout.
Ozrit also provides 24/7 support after launch. Multi-country platforms operate across time zones. Issues can emerge at any time. Having a team that can respond quickly reduces downtime and limits the impact of problems.
The team size varies based on program scope, but Ozrit typically works with teams of fifteen to forty people on large multi-country programs. This is large enough to handle complexity but small enough to maintain clear communication and accountability.
Testing and Validation Across Markets
Building a multi-country platform is one thing. Proving that it works correctly in every market is another.
Testing must cover functional requirements, compliance rules, language and localization, payment processing, tax calculations, performance under load, and security across different regulatory environments. You cannot test everything manually. Automation is essential.
But automated testing for compliance is difficult. Many compliance requirements are not simple pass-fail checks. They involve judgment, context, and interpretation. For example, a privacy regulation may require that user consent is obtained in a clear and understandable way. What does that mean? How do you automate a test for clarity?
The answer is a combination of automated checks for technical compliance and structured review processes for subjective requirements. Automated tests can verify that data stays in the correct region, that required fields are present, that consent flows are triggered at the right time. Human review validates that the user experience meets the spirit of the regulation.
This is where having compliance specialists embedded in the team matters. They can design test cases that reflect real regulatory expectations. They can identify edge cases that automated tests might miss. They can work with legal teams in different countries to validate that the implementation is correct.
Governance and Change Management
A multi-country platform requires strong governance. Without it, the platform will drift into chaos as different teams make local changes that conflict with each other.
Governance starts with clear ownership. Who decides what is in the core platform and what can be customized? Who approves changes that affect multiple countries? Who resolves conflicts when local requirements contradict the global architecture?
There must be a decision-making framework. Changes that affect core functionality or compliance should require approval from a central architecture or compliance board. Local changes that do not affect other markets can be approved regionally. The framework must be clear and enforced consistently.
Documentation is essential. Every compliance requirement, every local customization, every architectural decision should be documented and accessible. Teams in different regions need to understand why things are built a certain way. New team members need to onboard quickly. Auditors need to verify compliance.
Change management processes must account for the fact that updates cannot always roll out to all countries at once. Some markets may need changes immediately. Others may need to delay due to local approvals or testing requirements. The platform must support versioning and controlled rollouts.
The Long View on Multi-Country Platforms
Large enterprises often underestimate the complexity of building platforms that operate across many countries with different compliance requirements. The technical challenges are significant, but manageable. The real difficulty is in the coordination, governance, and ongoing maintenance.
The enterprises that succeed are those that invest in the architecture upfront, involve compliance and legal teams early, build in flexibility from the start, and work with partners who have done this before. Multi-country platforms are not impossible. They are hard. And they require experienced teams who understand both the technology and the delivery process.
The payoff is worth it. A well-designed multi-country platform allows an enterprise to scale efficiently, enter new markets faster, maintain consistent user experiences, and reduce compliance risk. But getting there requires discipline, realistic planning, and the right execution partner.